The Omenabyte Blog
Notes from the build.
Field notes on shipping AI products, securing what you build, and running infrastructure with fewer moving parts. Everything here is tested before it ships — including the parts that turned out to be a bad idea.
LatestSecuritySep 20, 2026 · 9 min read
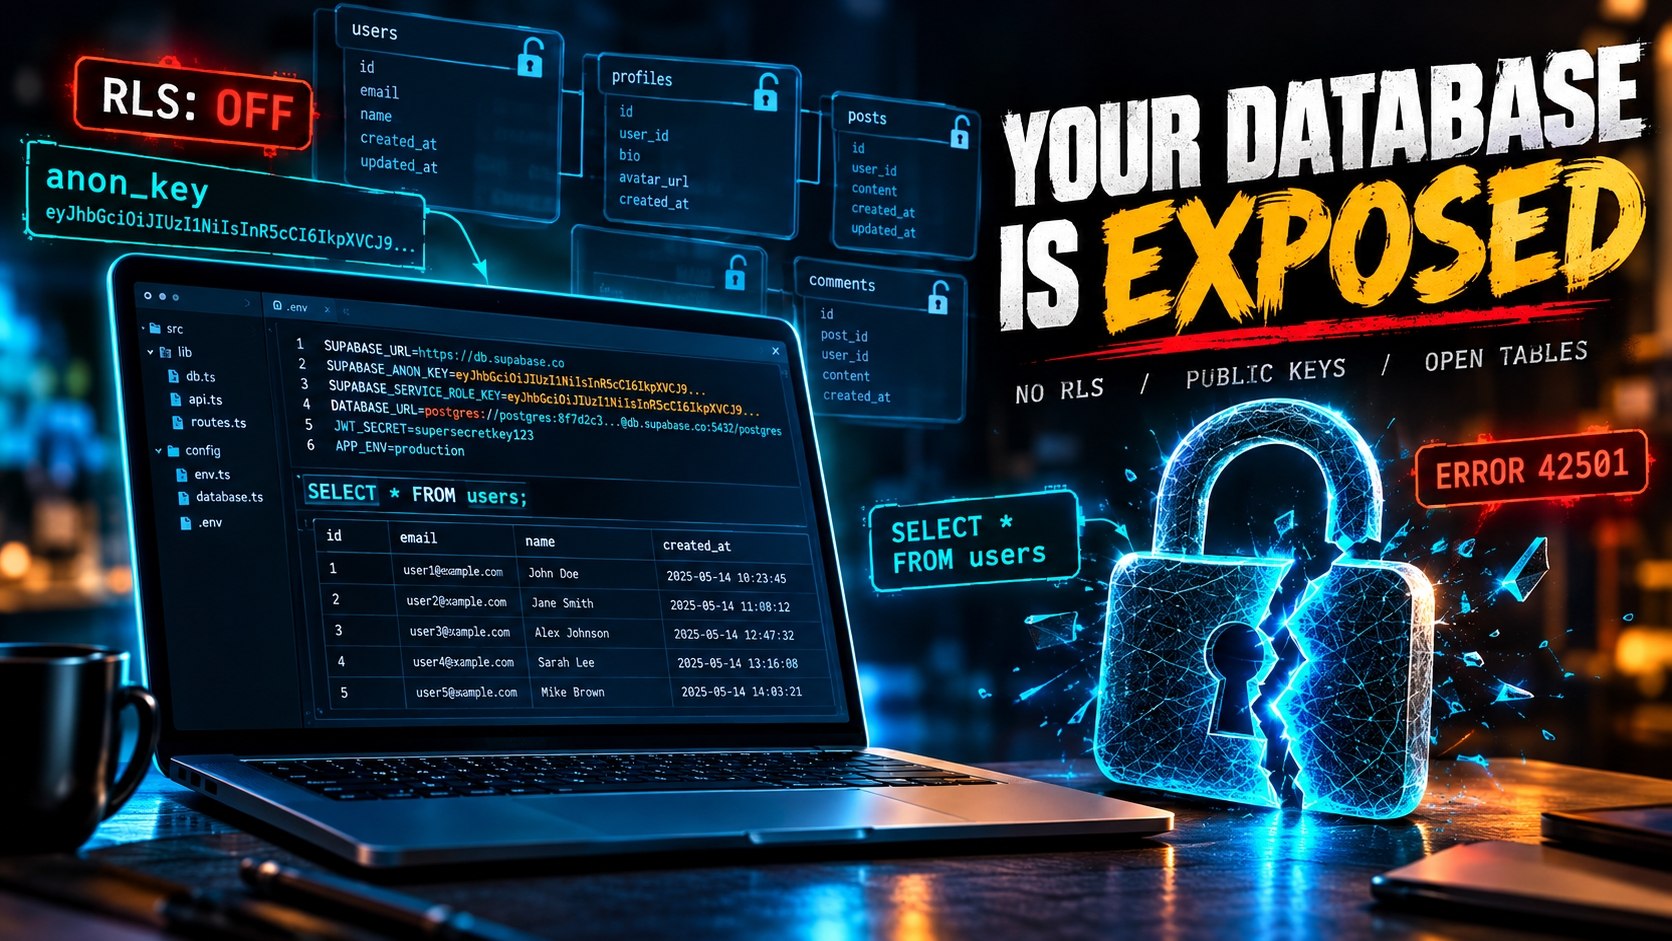
You're Doing Vibe-Coding Wrong. Here's the 17-Point Fix.
Scanners found 98% of AI-built apps have at least one security flaw. RLS off by default, API keys in JS bundles, open DELETE endpoints. The checklist that closes it.
Read the post →